
In a sweeping cybersecurity breach that has sent shockwaves through the North American logistics industry, 29 trucking companies across the United States and Canada have fallen victim to a coordinated phishing campaign, resulting in massive financial data leaks and a wave of ransomware demands.
Trucking Company Hacked – How It Happened?
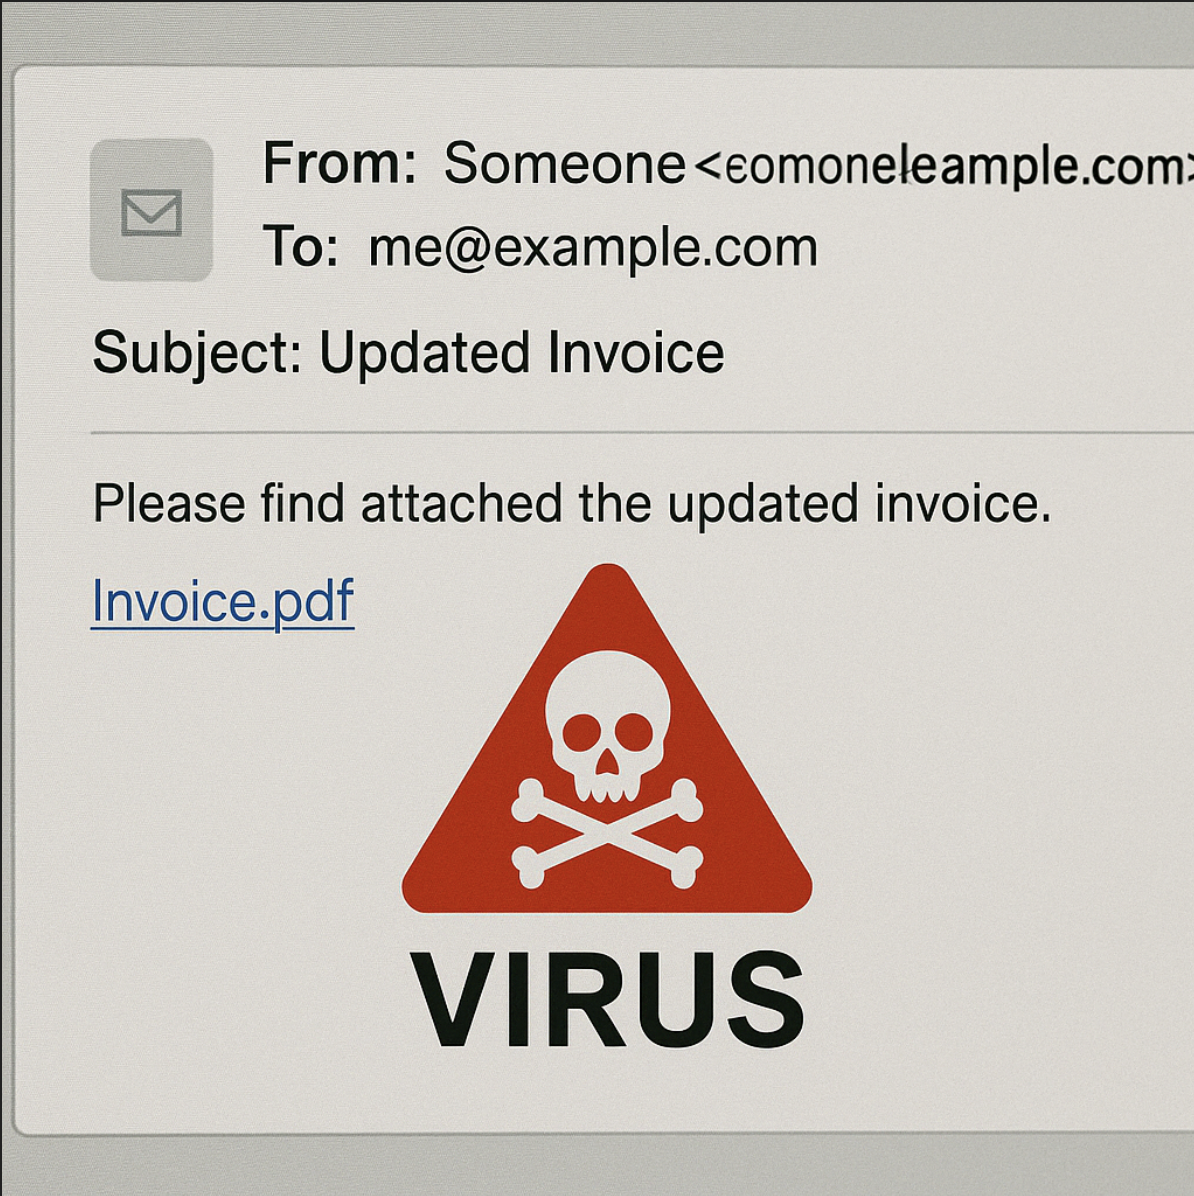
The attack, which cybersecurity experts believe originated from a sophisticated hacking group in Eastern Europe, began with what seemed like harmless emails sent to accounting and dispatch teams. The emails appeared to come from known industry partners, using subject lines such as:
- “Updated Fuel Surcharge Agreement”
- “Revised Broker Payment Terms”
- “New Compliance Deadlines from DOT/CCMTA”
Once opened, the emails prompted employees to download a PDF or Excel file. Hidden within these documents was a trojan-based malware, which silently infiltrated the companies’ internal systems.
What Was Compromised
Once inside, the hackers used advanced lateral movement techniques to access and exfiltrate key financial data, including:
Payroll databases
Carrier payment records
Fuel card credentials
Client invoice data
Internal banking credentials
Cybersecurity analysts confirm that over $15 million in payment data was exposed, with some companies reporting fake transactions being initiated from their bank accounts within 48 hours of the breach.
Ransomware Demands
Within days of the initial breach, infected companies began receiving ransom demands via encrypted messages left in system folders and sent directly to email inboxes. The attackers demanded payments ranging from $50,000 to $250,000 in Bitcoin, threatening to:
- Leak financial records to competitors
- Publish sensitive DOT compliance records online
- Permanently delete backups if the ransom was not paid within 5 days
Several companies attempted to negotiate, but experts warn that paying the ransom rarely guarantees full restoration.
Industry Fallout
The North American Trucking Alliance (NATA) issued a warning to its 8,000+ members to immediately audit their email security protocols and disable all macros and external content in Office documents by default. “This is the largest phishing-based ransomware attack in logistics history,” stated NATA spokesperson Jessica Lamont.
Two Canadian firms based in Ontario reported that their entire dispatch software was encrypted, paralyzing operations for nearly a week. One company in Ohio temporarily shut down its fleet of 47 trucks, citing inability to issue fuel cards or driver payments.
Cybersecurity Firms Respond
Security firm CyberMCS, which specializes in small to mid-size business protection, reports that none of its clients were affected. “Every day, hackers are evolving. Businesses that don’t adapt their cybersecurity are playing Russian roulette,” said CyberMCS CEO Martin Millowski.
Lessons Learned
This attack reinforces the importance of:
Staff phishing training
Two-factor authentication on all financial platforms
Daily backups stored offline
Real-time threat detection systems
As the industry works to recover, experts urge logistics companies to stop thinking of cybersecurity as optional. “You insure your trucks — it’s time to insure your data,” said Lamont.


Add comment