
WooCommerce is one of the most widely used eCommerce platforms in the world, powering millions of small and medium-sized online stores. Its flexibility, cost-efficiency, and open-source nature make it a favorite among business owners. But with that popularity comes risk—and many WooCommerce websites are dangerously underprotected.
Why Hackers Love WooCommerce Sites
Hackers specifically target WooCommerce because they know many store owners lack dedicated IT support. The platform depends heavily on plugins and third-party integrations. When these plugins go outdated or are poorly coded, they become easy entry points for cybercriminals. Even worse, many users never update their themes, plugins, or core WordPress files, creating a playground of vulnerabilities.
Cybercriminals use automated tools to scan the internet for these weak points. If your site has even one outdated plugin or misconfigured setting, it may already be listed on hacker forums without you knowing.
What Happens When They Get In
Once inside your WooCommerce website, hackers can extract customer data, including names, emails, passwords, and even payment details. This data is either sold on the dark web or used for phishing scams that can destroy your customers’ trust in your brand.
Some attackers go further and install ransomware, locking you out of your website until you pay up. These attacks often encrypt your entire site—products, customer records, orders, everything—and you’re left with no access unless you meet their demands. Even then, there’s no guarantee they’ll release your data.
In many cases, hackers don’t even want your data—they want your website. They can use your WooCommerce store as a base to send spam, launch phishing campaigns, host malware, or infect your customers. All of this damages your reputation and may lead to your domain being blacklisted.
DDoS Attacks on WooCommerce Websites
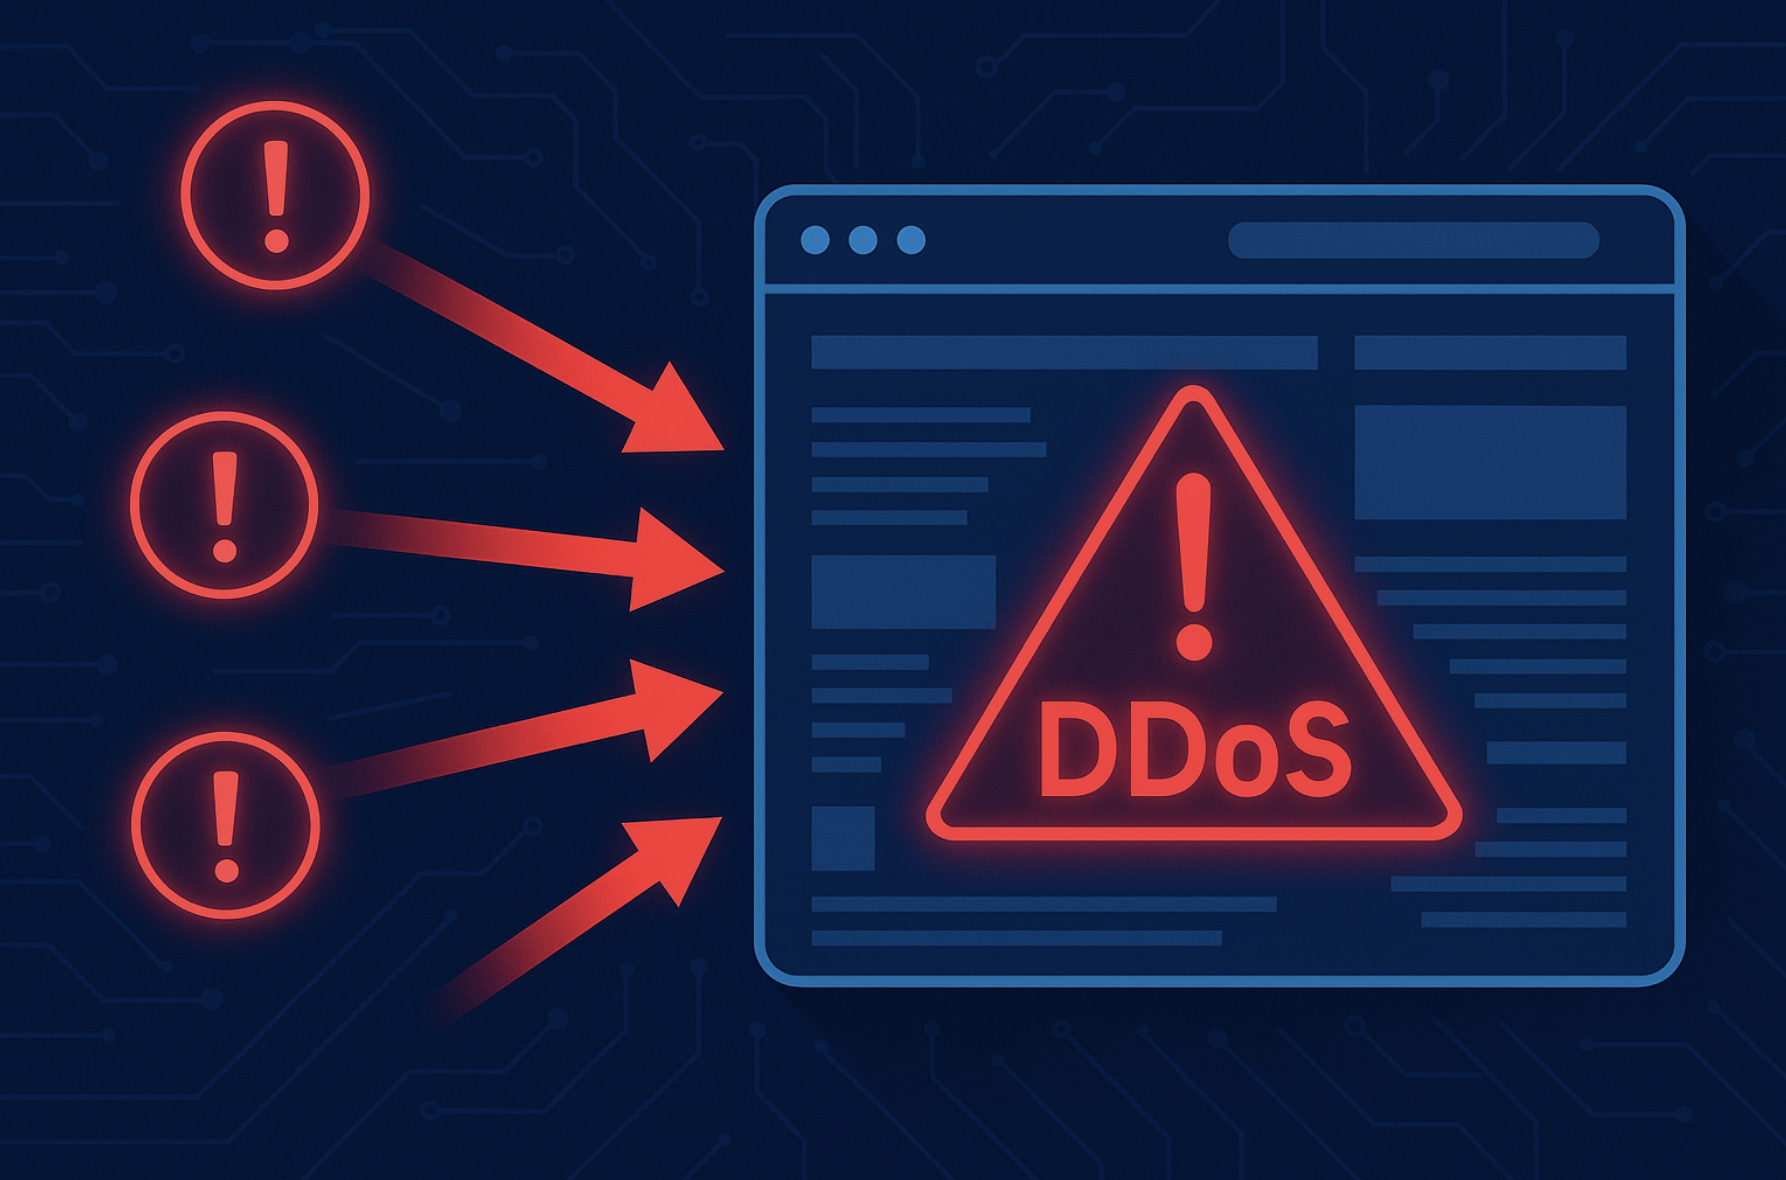
Most online store owners worry about credit card fraud or data leaks, but few truly understand the devastating power of a Distributed Denial-of-Service (DDoS) attack. These attacks don’t need to steal your data to destroy your business—they just need to take you offline.
In a DDoS attack, hackers flood your website with massive amounts of fake traffic from multiple sources. Your server becomes overwhelmed, leading to crashes or severe slowdowns. Customers can’t browse, add items to cart, or make purchases. During the attack, your revenue drops to zero—and the longer it lasts, the more damage it causes.
Here’s what can happen if your WooCommerce site is hit with a DDoS:
Instant website crash — Your server gets overwhelmed and goes offline within seconds.
Total loss of sales — No one can browse or buy while your site is down.
Damage to your reputation — Customers see your site offline and may assume you’re hacked or unreliable.
Loss of SEO rankings — Google may penalize your search rankings due to prolonged outages.
Burned ad spend — Ongoing paid traffic is wasted if your site can’t load.
Ransom demands — Some attackers will email you mid-attack demanding payment to stop.
Vulnerability stacking — A DDoS is often just step one, followed by deeper exploits or ransomware injection.
Worse yet, these attacks are shockingly easy to launch. Cybercriminals don’t need advanced coding skills anymore. Today, anyone with $10 and access to a DDoS-for-hire platform can rent a botnet and take your WooCommerce store offline for hours.
WooCommerce Sites Are Especially Vulnerable If:
You’re using shared or budget hosting
You don’t have a firewall or CDN protection in place
Your site has no active traffic monitoring or automated throttling
You rely on dozens of third-party plugins, increasing potential entry points
If this sounds like your setup—you’re at risk, whether you realize it or not.
The Hidden Cost of an Unprotected Site
An insecure WooCommerce site isn’t just a technical issue. It’s a financial one. Recovering from a breach can cost thousands in lost sales, customer refunds, legal liability, and clean-up fees. You may face GDPR or CCPA fines if customer data is exposed. Worse, once your store is compromised, customers may never return.
Get a Free WooCommerce Security Check Today
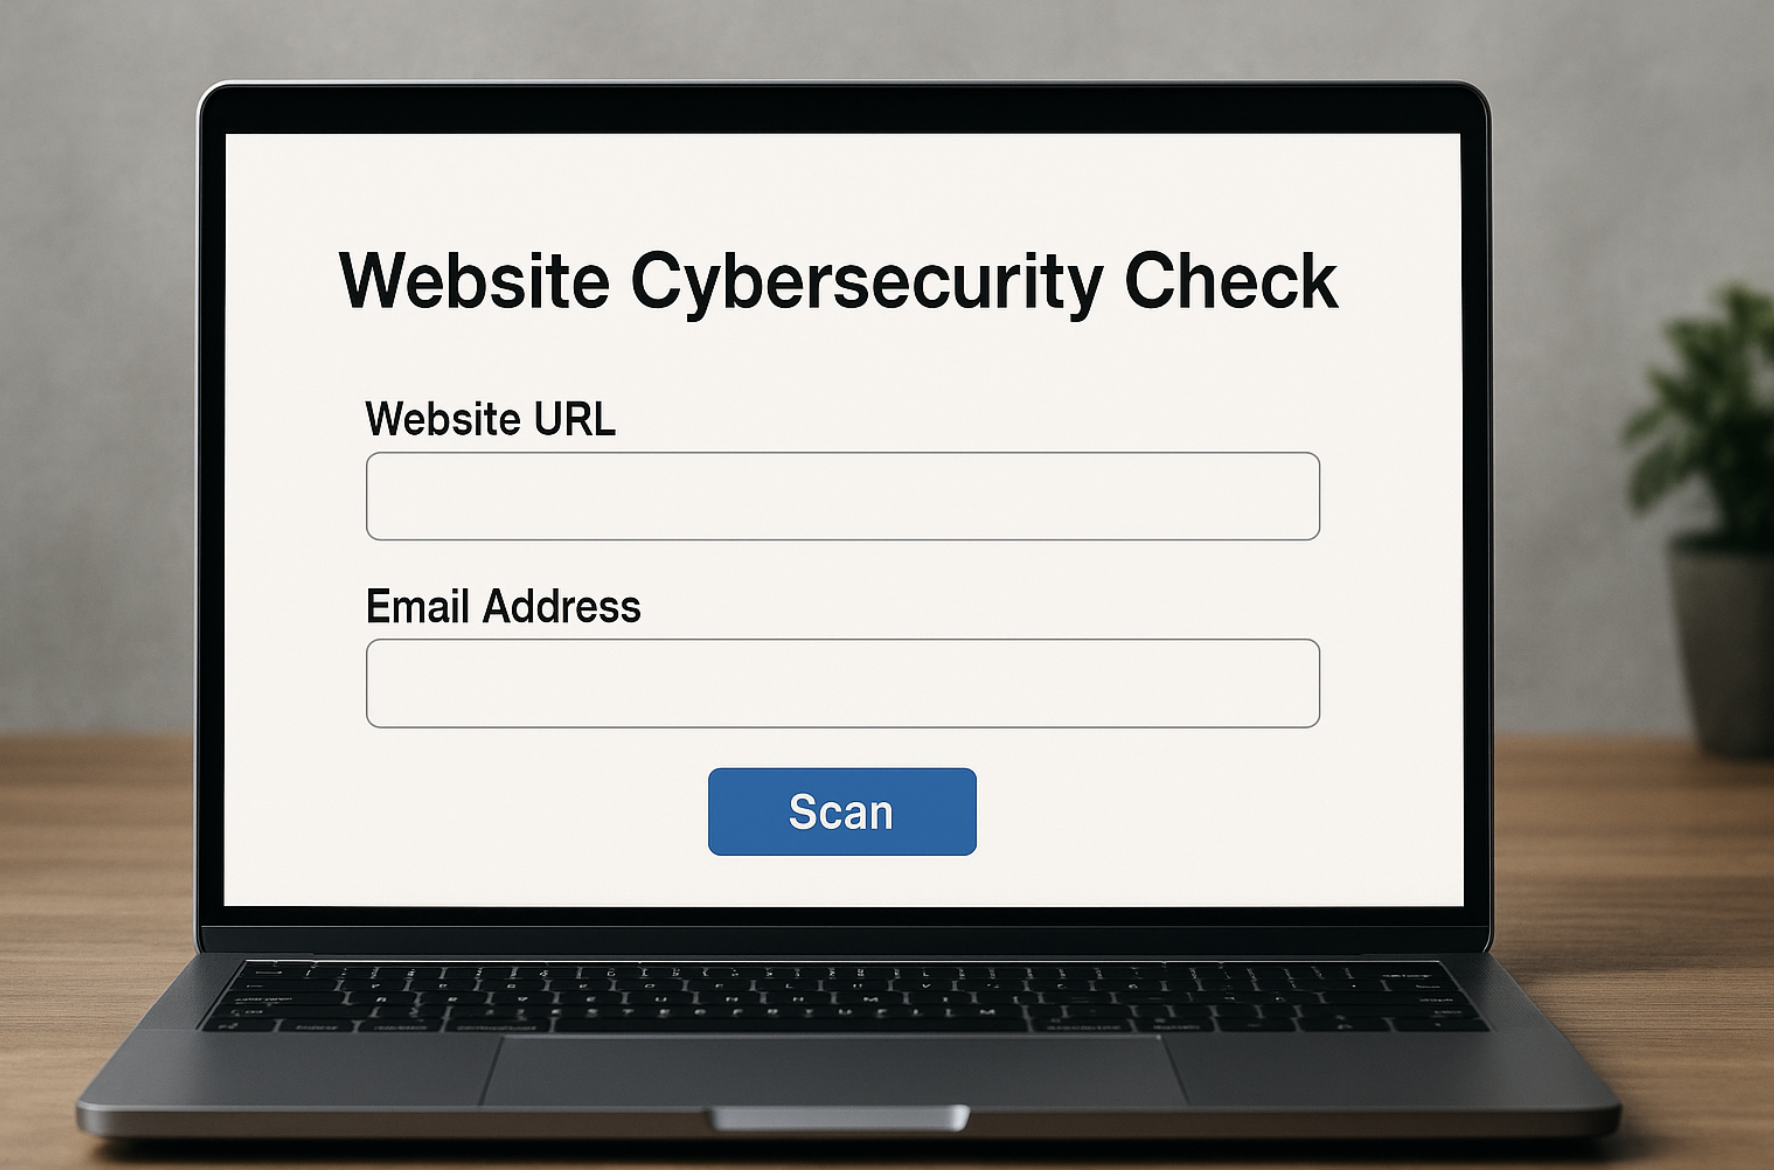
If you’re running a WooCommerce site and you haven’t actively secured it, you’re at risk—and you may not even know it. That’s why Cyber57 offers a completely free WooCommerce cybersecurity check. It’s fast, non-invasive, and gives you instant insight into your store’s vulnerabilities. No technical knowledge required.
Just go to Cyber57.com, enter your site, and in under a minute, you’ll know if your business is safe—or if you’re in danger without realizing it.
Hackers are already scanning. It’s just a matter of time before they find you. Don’t wait to become a victim. Check your WooCommerce security today—free at Cyber57.com.


Add comment